ACL Rules with NetPilot
NetPilot can propose adding, changing or removing an ACL rule on an edge's interface, or creating a new ACL. You apply the change on its card: see Changing Configuration with NetPilot for how proposals work and the rights you need (Update to add, change or remove a rule, Create for a new ACL).
Block something on an interface
NetPilot adds a deny rule before the ACL's closing permit any, so everything else still gets through. The card shows the whole ACL after the change, with the new rule highlighted:
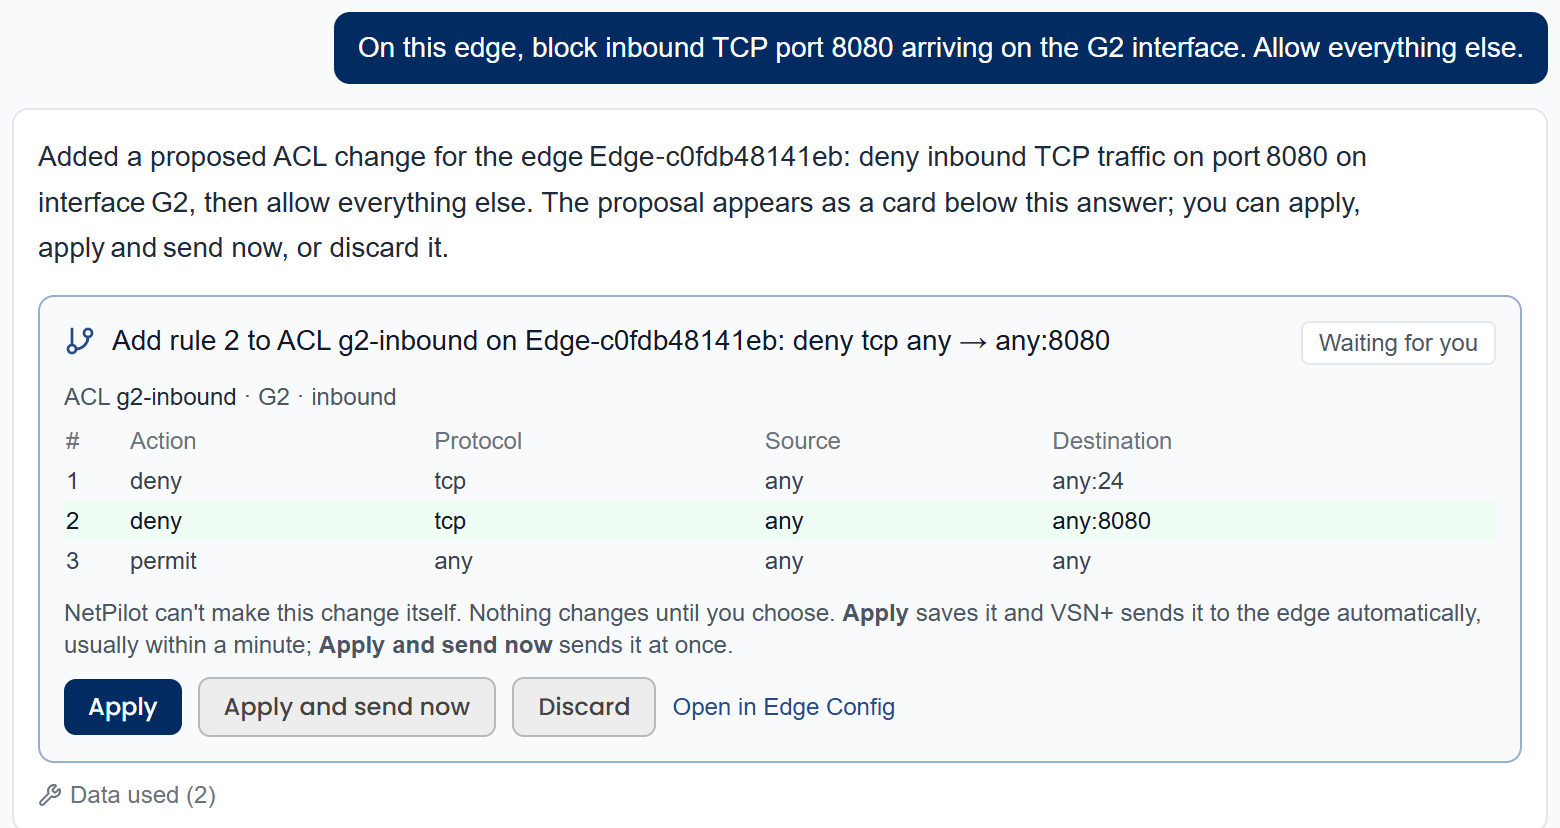
- Block inbound TCP port 3389 arriving on G2 on this edge. Allow everything else.
- On this edge, deny inbound traffic from 192.168.99.0/24 on G1.
- Block inbound UDP 161 to 10.30.0.0/24 on G2.
Allow only certain traffic
An allowlist: say only explicitly, as everything else is then dropped. NetPilot can do this only as a new ACL, so only on an interface with no ACL yet; to turn an existing ACL into an allowlist, edit it in Edge Config.
- On G1, allow only TCP 443 and DNS (UDP 53) inbound; drop everything else.
Change a rule
Rules are numbered as in Edge Config.
- In ACL g2-inbound, change rule 1 to block TCP port 25 instead of 24.
- Make rule 1 of g2-inbound apply only to source 192.168.10.0/24.
Remove a rule
- Remove rule 1 from ACL g2-inbound on this edge.
- Remove the TCP 24 block on G2.
Create a new ACL
Only on an interface that has no ACL yet.
- Create an inbound ACL on G1 that blocks TCP 23 and allows everything else.
Tips
- Say the interface (G1, G2 …), the direction (inbound if you don't say), the protocol (TCP, UDP, ICMP or any) and one port per rule. Port ranges such as 1000-2000 are not supported.
- If the interface already has an ACL, NetPilot adds the rule to that ACL instead of creating a second one. The ACL keeps its name, so a name that no longer fits (for example one created to block telnet) can be changed in Edge Config.
- Not sure what's there? Ask "Show me the ACLs on this edge" first.
What NetPilot refuses
NetPilot won't propose these, and the console shows Not proposed with the reason:
- blocking tunnel or VPN traffic on a WAN interface (UDP 51820/51821, 500/4500);
- opening a WAN interface to the whole internet inbound;
- leaving a LAN interface dropping all traffic, unless you asked for an allowlist;
- a permit any that would come before a later ACL on the same interface, so that ACL would never be used;
- a new ACL on an interface that already has one (NetPilot adds a rule to the existing ACL instead);
- outbound ACLs on a WAN interface;
- ACL changes on TAP-bridge edges (for now);
- any change while configuration changes are turned off for your tenant.
These can be made by hand: see ACL in Edge Configuration.